Event Participation

360 Cyber — Full Lifecycle Cybersecurity

Acropolis Integro Participation
April 15, 2026 JW Marriott Absheron, Baku
Back to list

The Acropolis Integro team participated in 360 Cyber — a full lifecycle cybersecurity conference organized by B&B Security at the JW Marriott Absheron hotel in Baku. The event brought together over 300 guests, 20 speakers, and 30 experts from telecom, finance, oil & gas, and other critical sectors.

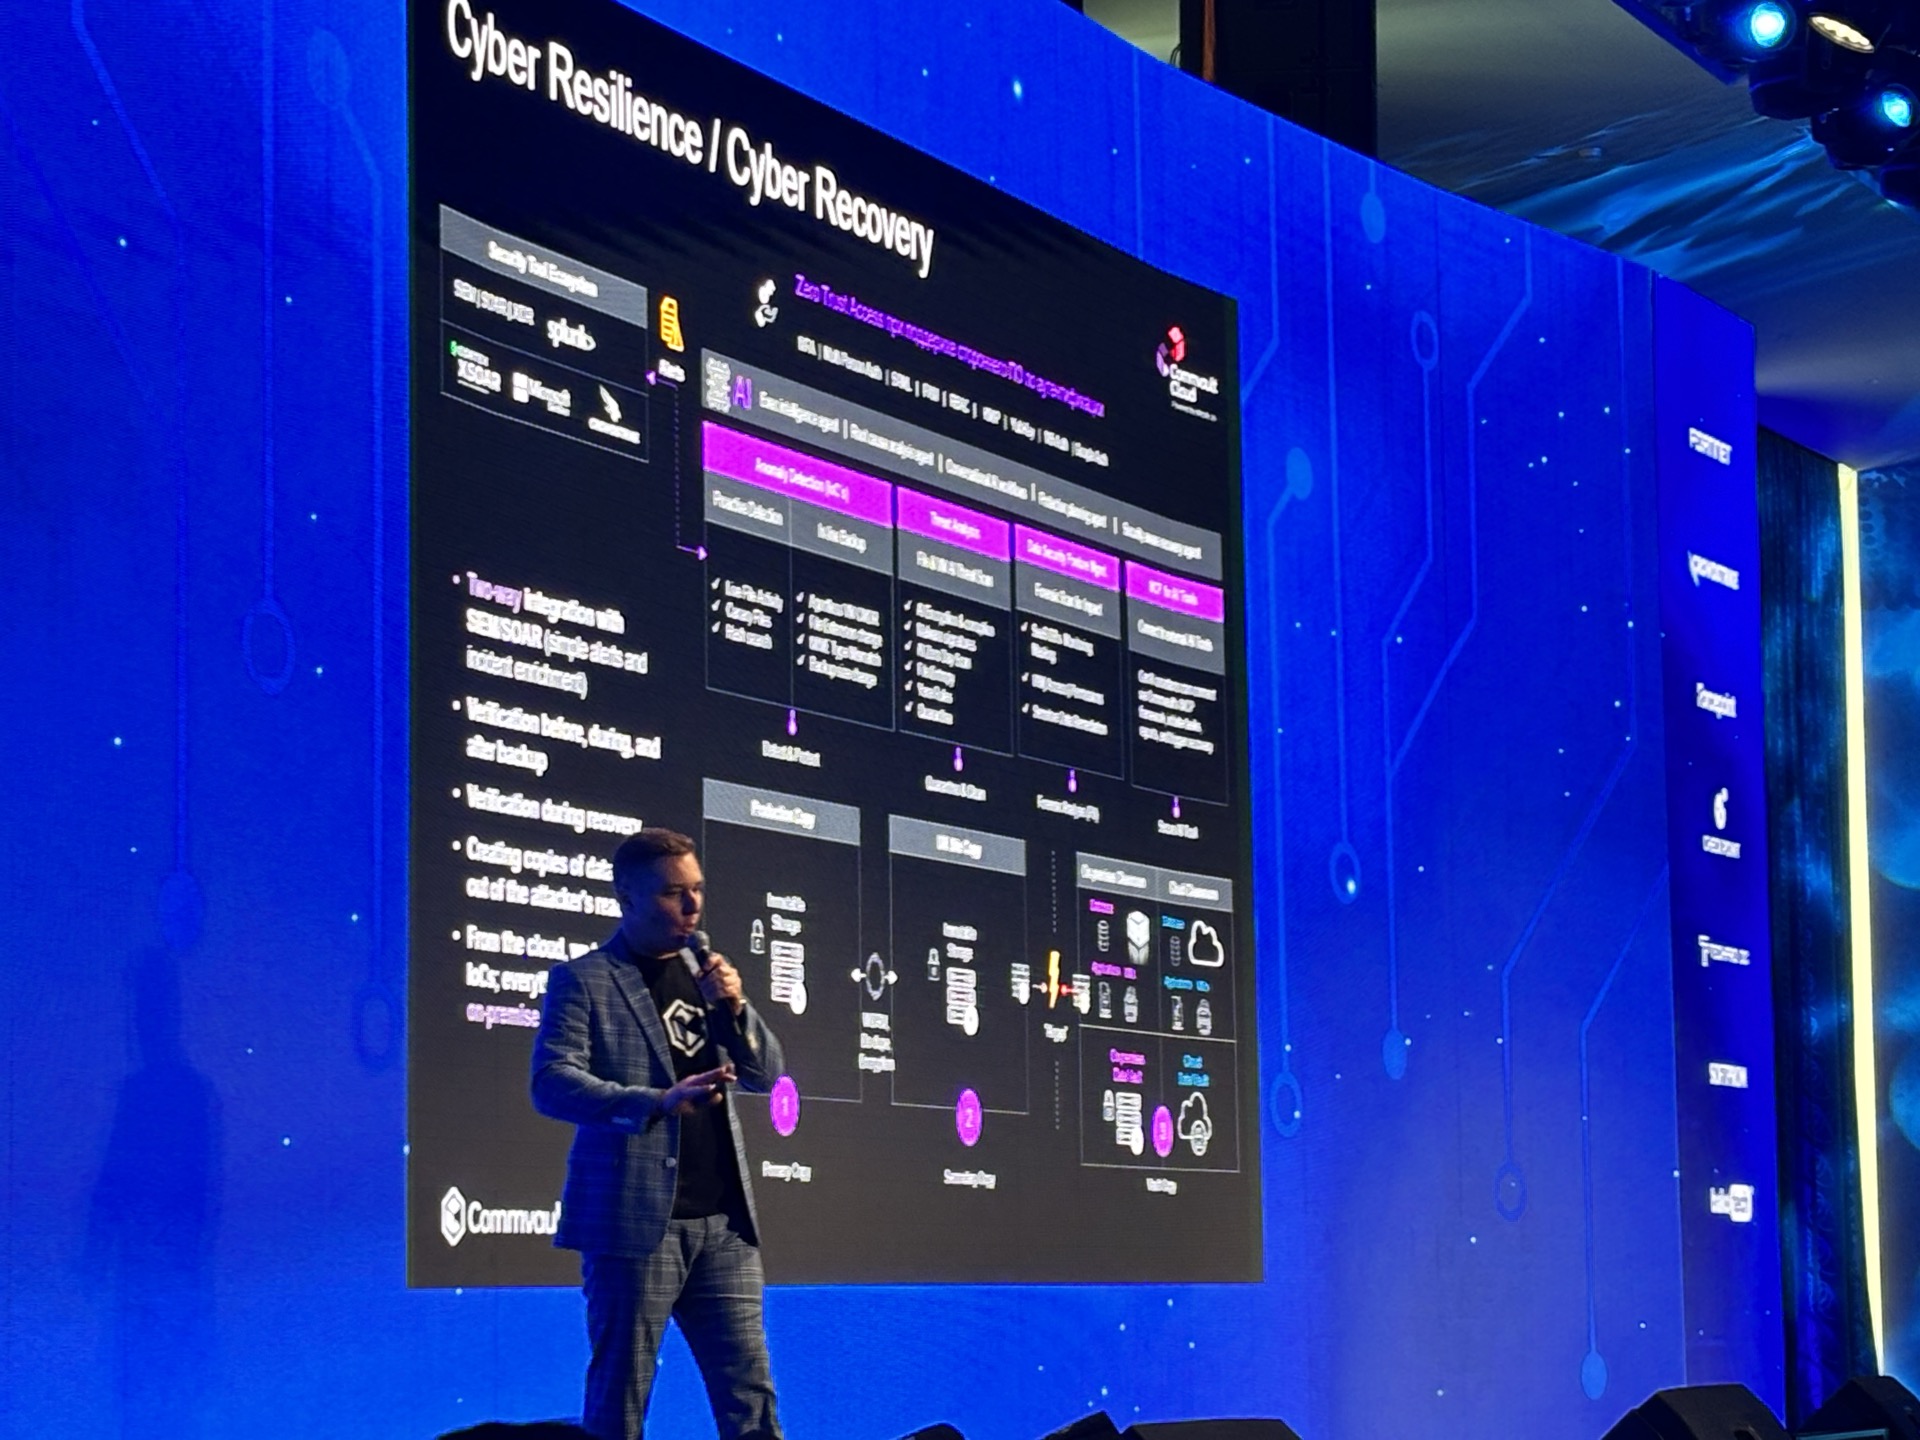
Commvault presented solutions in cyber resilience and data protection. Evgeny Pukhov covered Cleanroom Recovery, Threat Scan, and the “Real Clean” concept — restoring without losing post-attack improvements. Splunk showcased a unified TDIR platform with Risk-Based Alerting and an AI Assistant; CyberArk outlined the four pillars of Identity Security with Zero Standing Privileges; Opinnate presented its NSPM platform with the Opi AI copilot and a 90% reduction in manual policy audits; and B&B Security covered SOC transformation with agentic AI amid an 89% rise in AI-enabled attacks.

The key takeaway: modern cybersecurity is not a collection of disjointed products but a continuous lifecycle — “Assess → Protect → Detect → Respond → Improve” — that unifies data, identity, and infrastructure protection into a single architecture. The event concluded with two panel discussions and a gala dinner.

Presentations

AK
Anar Khanaliyev
B&B Security

360° Cybersecurity Strategy

Full defense lifecycle: Assess → Protect → Detect → Respond → Improve
Integrated architecture instead of disjointed point products
Focus on critical sectors: banking, telecom, oil & gas
Partner ecosystem: 10+ global vendors in a single platform
VR
Vusal Ramazanlı
B&B Security

360° Cybersecurity Strategy

Assess + Protect phases: continuous attack surface evaluation
Continuous Security Validation via BAS (Cymulate)
Risk-Based Prioritization at the asset and process level
Regulatory compliance: financial and energy sectors
AG
Aydın Gurbanlı
B&B Security

Agentic SOC Operations Transformation

89% increase in AI-enabled attacks, yet 70% of teams lack integrated AI
Agentic AI: autonomous agents for triage and investigations
Up to 3× MTTR reduction with AI assistants like CrowdStrike Charlotte AI
Analyst role shift: from alert handling to decision-making
EP
Evgeny Pukhov
Commvault

Business Continuity After Cyberattacks

Commvault Cleanroom Recovery — isolated environments for recovery testing without production risk
Threat Scan: identifies compromised files and restores clean versions
99% faster recovery, 30× more frequent DR testing
Identity Resilience: account recovery and rollback
Real Clean Recovery — preserves post-attack improvements instead of a full rollback
SO
Serkan Ozden
Opinnate

Firewall Policy Management & Risk Visibility

NSPM platform for on-prem and cloud firewalls (AWS, Azure, GCP)
Shadow rule analysis + usage monitoring with 90-day topology context
90% reduction in manual policy audits
Opi — AI copilot with natural language policy queries
Built-in compliance reports: PCI-DSS, HIPAA, ISO 27001
CM
Cem Men
Splunk

Unified Threat Detection

Splunk Enterprise Security + SOAR + UEBA in a unified TDIR platform
Risk-Based Alerting: −90% alert volume with higher true-positive rate
Detection Studio with MITRE ATT&CK coverage
AI Assistant: SPL query generation, investigation summaries
55% faster resolution, 64% more efficient SecOps, 111% more accurate detection
BA
Bugrahan Adamhasan
CyberArk

Identity-Focused Security

79% of enterprises experienced an identity-related breach in the last 2 years
Four pillars: PAM, Secrets Management, Workforce Identity, Customer Identity
Zero Trust / assume-breach: verify identity + validate device + least privilege
Just-in-Time access and Zero Standing Privileges for privileged sessions
AI-driven detection of misconfigured and unused permissions in the cloud

Key Takeaways

Assessment & Protection
360° lifecycle approach
Continuous Security Validation
Firewall policy management
Detection & Response
Unified TDIR (SIEM + SOAR + UEBA)
Agentic AI in the SOC
MITRE ATT&CK coverage
Identity & Access
PAM and Secrets Management
Zero Standing Privileges
Machine identity protection
Resilience & Recovery
Cleanroom Recovery
Identity rollback
Real Clean Recovery

Recommendations

Immediate Actions

1 Run a Breach & Attack Simulation to measure real-world defenses
2 Audit firewall policies: shadow rules, unused rules, compliance reports
3 Measure current SOC MTTD/MTTR and identify bottlenecks
4 Inventory privileged accounts and machine identities

Strategic Initiatives

1 Deploy a unified TDIR platform with AI assistant (SIEM + SOAR + UEBA)
2 Consolidate the identity plane around PAM and Secrets Management
3 Adopt Cleanroom Recovery with regular restore testing
4 Integrate agentic AI into SOC operations to reduce MTTR
5 Build a 360° architecture: Assess → Protect → Detect → Respond → Improve

Recommended Technology Stack

Commvault Cleanroom
Cyber Recovery
Splunk ES + SOAR
Unified TDIR
CyberArk PAM
Identity Security
Opinnate NSPM
Policy Automation

Want to learn more about cybersecurity solutions?

Discuss infrastructure solutions with Acropolis Integro experts